Encoding
100% in your browser
JWT Decoder
Decode JSON Web Tokens instantly. Reveals the header, payload, and signature. Works offline — your token never leaves the browser.
⚠️ This tool does not verify the signature. Only use it to inspect token contents — never to validate authentication.
JWT Decoder
Paste any JSON Web Token to instantly decode its three parts: the header, the payload, and the signature. Expiry (exp) and issued-at (iat) timestamps are formatted as human-readable dates.
JWT structure
A JWT consists of three Base64URL-encoded parts separated by dots: header.payload.signature
- Header: specifies the token type (
typ) and signing algorithm (alg) — e.g. HS256, RS256. - Payload: contains the claims — user identity, roles, expiry, and any custom data.
- Signature: a cryptographic hash that verifies the token was not tampered with. This tool does not verify signatures.
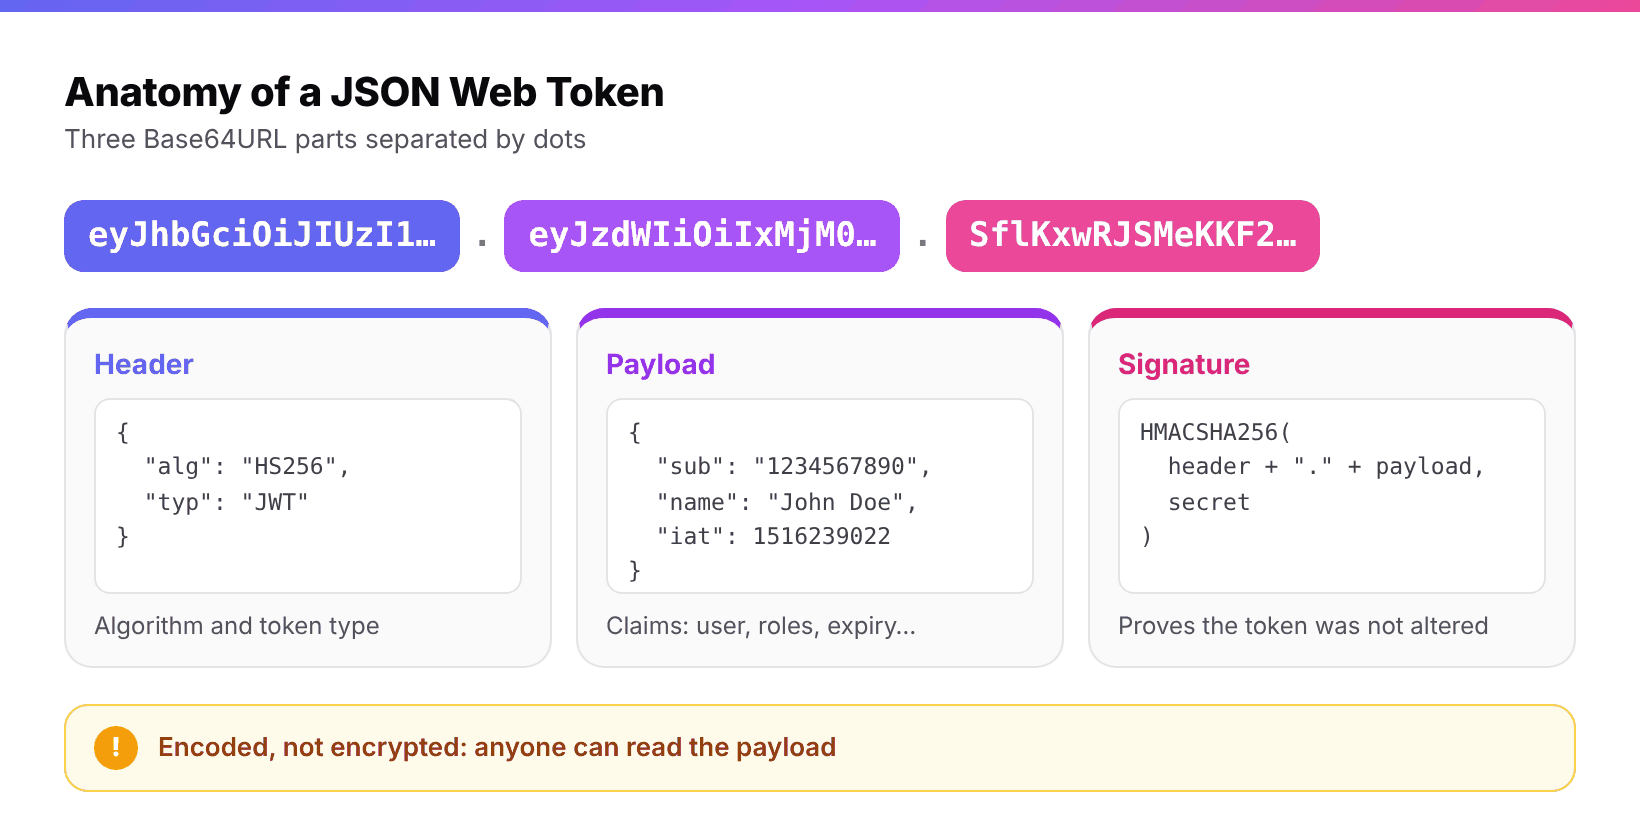
The payload is only Base64URL-encoded, so anyone can read it: never store secrets in it.
Common JWT claims
sub— subject (user ID)iss— issueraud— audience (intended recipient)exp— expiration timestamp (Unix time)iat— issued-at timestampnbf— not-before timestampjti— JWT ID (unique identifier)
Security note
JWT payloads are only Base64-encoded — not encrypted. Never put sensitive information in a JWT unless you use JSON Web Encryption (JWE). Always verify signatures server-side.